IMDEA Networks
NEXTONIC hosts the proof of concept of a hardware-rooted approach to digital sovereignty in cloud and edge infrastructures
NEXTONIC hosted the proof of concept of a security architecture that replaces IP address evaluation with cryptographically verifiable, hardware-anchored workload identity, developed by Red Hat, Telefónica and JPMorganChase researchers
17 September 2026
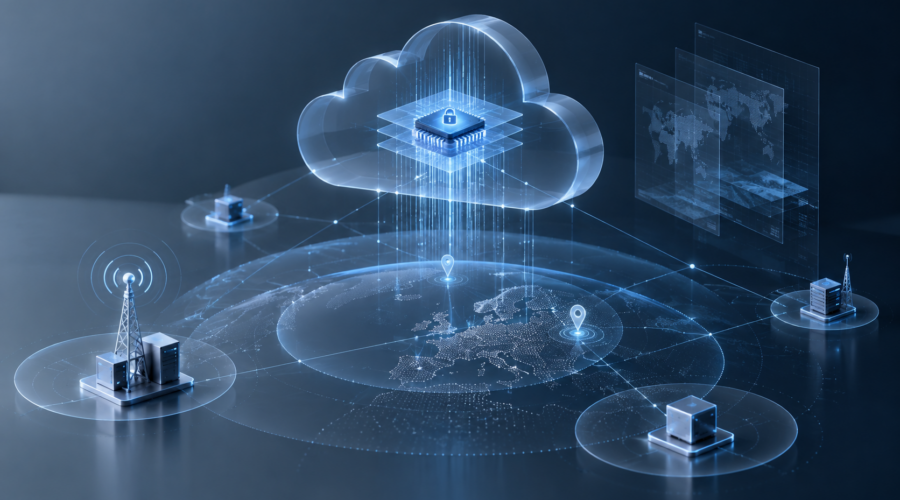
The NEXTONIC laboratory, the open 5G/6G innovation facility co-founded by IMDEA Networks Institute and Telefónica, has hosted the proof of concept (PoC) of a new security architecture that replaces IP address evaluation with cryptographically verifiable, hardware-anchored workload identity. The results of the joint work, carried out with Red Hat, Telefónica and JPMorganChase, have been published on the Red Hat blog under the title Substituting IP address evaluation with hardware-rooted sovereign zero trust.
Today, most organisations still rely on the IP address to evaluate access rights to sensitive data, especially in what relates to location, i.e., to identify where those data is being accessed from. That model is fragile, expensive to operate and, critically, easy to spoof: a VPN is enough to make a workload appear to be running inside a permitted jurisdiction when it is not. As national and regional regulations tighten the conditions on where data may reside and who may process it, an identifier that cannot be proven becomes a compliance liability rather than a control.
The approach demonstrated at NEXTONIC addresses this at the root. It combines open workload identity based on SPIFFE/SPIRE with TPM-based attestation, binding each workload to the physical platform on which it runs and to the devices attached to that platform — including its source of geolocation, provided by a trusted party via a CAMARA network location API. The result is a verifiable geofence: an attestation, signed by hardware, that a given workload is genuinely executing within a given territory. Access policies can then be enforced on evidence rather than on assumption and revoked automatically if a workload moves outside the authorised perimeter.
The contribution of NEXTONIC has been decisive in this second stage. The laboratory provided the mobile network environment in which the spoof-resistant geolocation was produced and validated, allowing the concept to be exercised end to end over realistic 5G infrastructure rather than in simulation alone. This is precisely the role the facility was created to play: turning architectural proposals into demonstrable, reproducible results before they reach the standards bodies and the market.
For Europe, the implications go beyond security engineering. Digital sovereignty has so far been asserted largely through contractual and jurisdictional means; this work makes it technically demonstrable. An operator, a bank or a public administration can prove — cryptographically, continuously and without trusting the declaration of any intermediary — that regulated data has been processed only on authorised hardware within authorised borders. Sovereignty ceases to be a statement of intent and becomes an auditable property of the infrastructure itself.
The architecture is built entirely on open source and open standards, and is already feeding industry work including the IETF draft on verifiable geofencing and the Linux Foundation’s AegisEdgeAI project.
“For Telefónica, digital sovereignty cannot remain a contractual promise: it has to become a property of the network that we can prove, continuously and to any auditor,” said Diego López, the researcher at Telefónica in the project and a member of the NEXTONIC board. “What this proof of concept shows is that hardware-rooted workload identity lets an operator demonstrate exactly where regulated data has been processed, on which platform and within which borders.
Recent Comments